

CSIRT procedures and escalation
We define who detects, who isolates affected systems, how logs are preserved and who approves internal and external communication.
DNSC has started fining unregistered organizations, up to RON 500,000 for failing to notify.
For DNSC incident reporting you have 24 hours for the early warning. We prepare CSIRT procedures, the PNRISC reporting flow, backups and exercises, for teams across Romania.
Get a quote for procedures, reporting and exercises.
WHY STOREWEB
Since 2008 we have worked with the servers, networks and data of companies and public institutions across Romania. We do cybersecurity on infrastructure we manage every day.
Every project is tailored to your organization's size, infrastructure and sector.
We define who detects, who isolates affected systems, how logs are preserved and who approves internal and external communication.
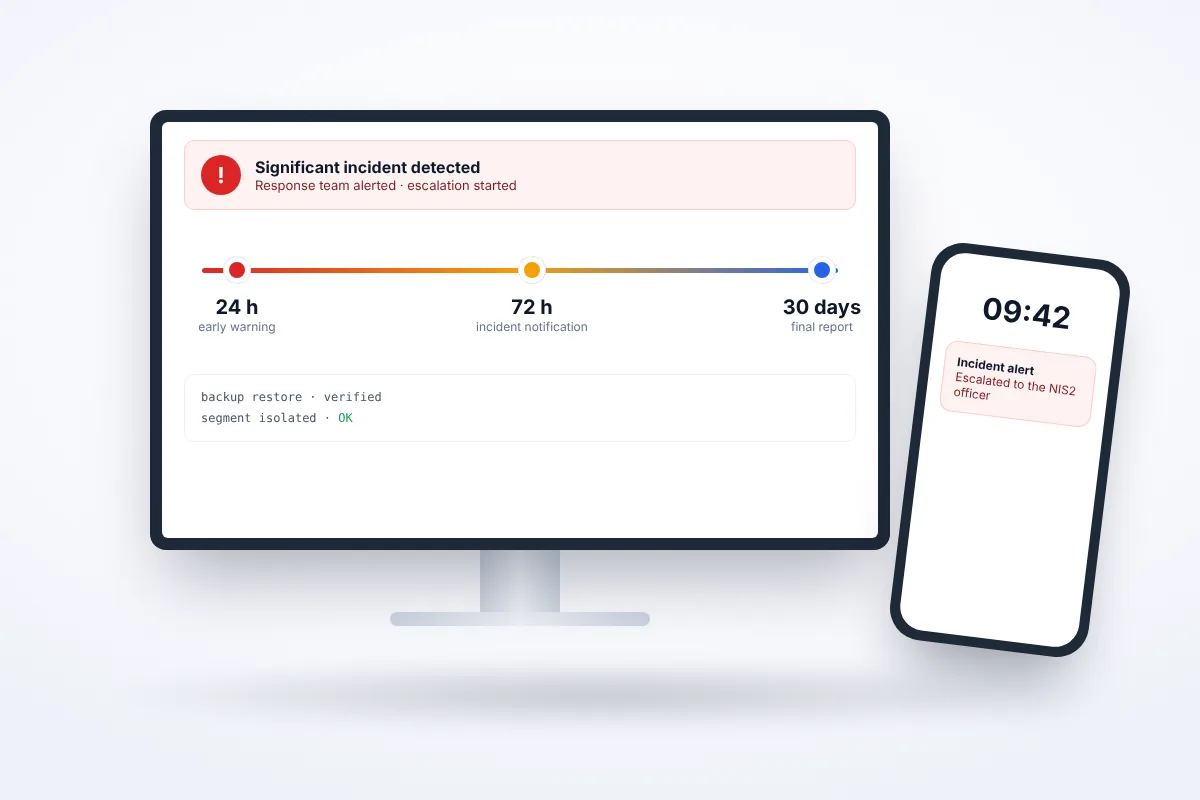
We prepare the forms and severity criteria for the 24h early warning, the 72h incident report and the final report within 30 days.
We check backup and disaster recovery strategies and run staff and management training, including phishing simulations.
The study “Radiografia Securității Cibernetice în România în 2026” (FORT, 211 organizations) shows that 15% of participants had eight or nine of the nine technical measures analysed, yet had never tested their incident response plan.
Who declares the incident, who talks to DNSC and who stands in for each person when absent. The list must also exist on paper.
An untested backup is an assumption. It is worth measuring how long restoring a critical system really takes.
The 24-hour, 72-hour and 30-day deadlines require information you must be able to gather quickly: which systems, which data, what impact.
Incident response procedures are among the measures checked in the NIS2 gap analysis. If your organization is not registered yet, the first step is the notification to DNSC.
What DNSC incident reporting means, how CSIRT reporting through PNRISC works and what must be in place before the first incident.
Essential and important entities report significant incidents to DNSC through the PNRISC platform. Reporting has three mandatory moments: an early warning within 24 hours, an incident notification within 72 hours and a final report.
The clock starts when you become aware of the incident, not when the investigation ends. Without a written procedure, the first hours are lost asking who decides.
Law no. 124/2025 clarified what a significant cybersecurity incident is. Your procedure must state who assesses the incident, on which criteria and how quickly the reporting decision is made.
We build these criteria around your actual operations, so the team neither reports every alert nor misses an incident that should have been reported.
CSIRT reporting is done on DNSC's national PNRISC platform. Within 24 hours you send the early warning, within 72 hours the notification with the initial assessment, and the final report no later than one month after the notification.
We prepare templates with the required data in advance, so on the day of the incident you fill them in instead of searching for information.
CSIRT procedures set out roles, the escalation chain, deputies, communication channels and the technical steps for containment, investigation and recovery.
We write them for your infrastructure, not from a generic template, and link them to the NIS2 gap analysis and to the measures checked during the audit.
An untested backup is an assumption. We check what is backed up, where, how often and how long it takes to restore a critical system.
The continuity plan states what keeps running during the incident, how people work and in which order systems are restarted.
NIS2 requires management to attend training and all staff to be trained regularly. We run role-based training and phishing simulations with measurable results.
We work remotely or on site with teams across Romania. Fill in the form above and get a quote for procedures, reporting and exercises.
Under GEO no. 155/2024, essential and important entities send the early warning within 24 hours, the incident report within 72 hours and the final report within one month.
No. Consulting helps your organization build internal detection, response and reporting procedures towards the competent authorities and CSIRT teams.
Yes. Articles 12-14 of GEO no. 155/2024 set out management accountability and mandatory cybersecurity training and awareness, including against phishing attacks.
The affected entity reports the significant incident through PNRISC. STOREWEB prepares the procedure, templates and team, and provides technical support for reporting when needed.
Yes. We deliver procedures, training and exercises remotely or on site, for companies and institutions across Romania.
Each step prepares the next one. You can start with any of them, depending on where your organization is now.
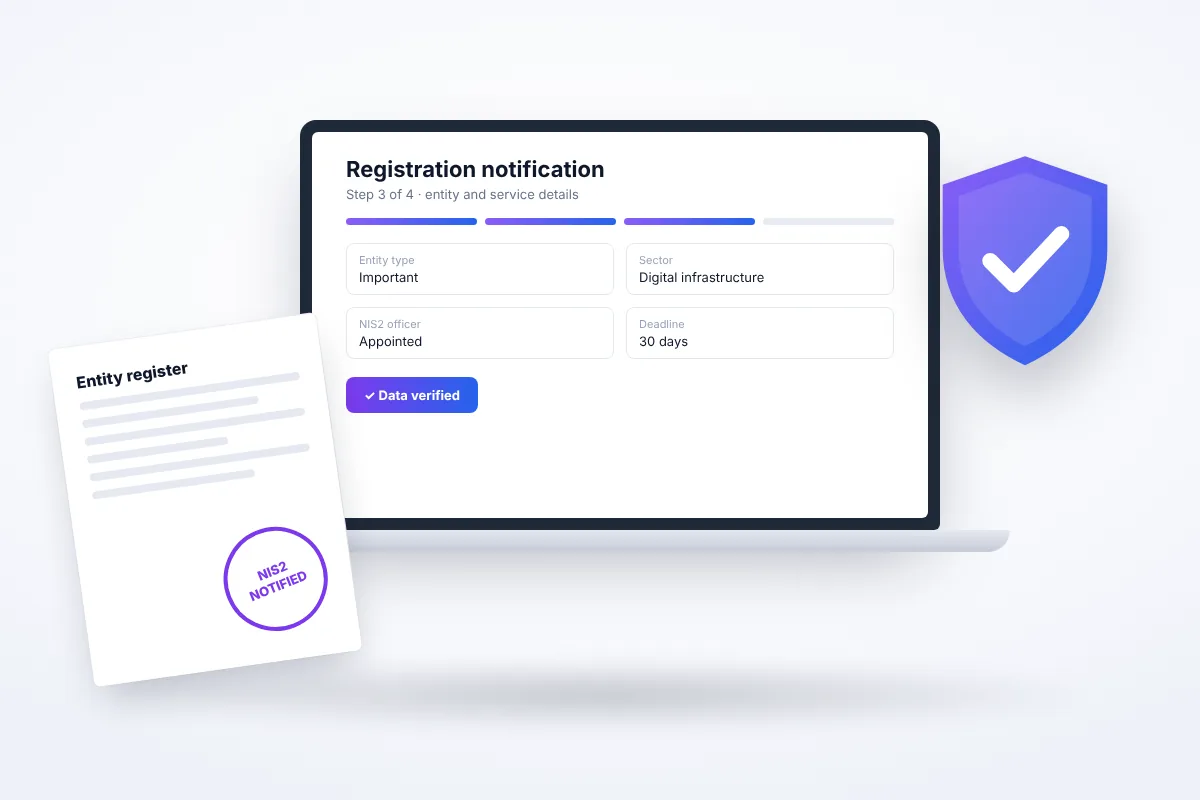
Find out whether NIS2 applies and notify DNSC within the 30 days.
See what's included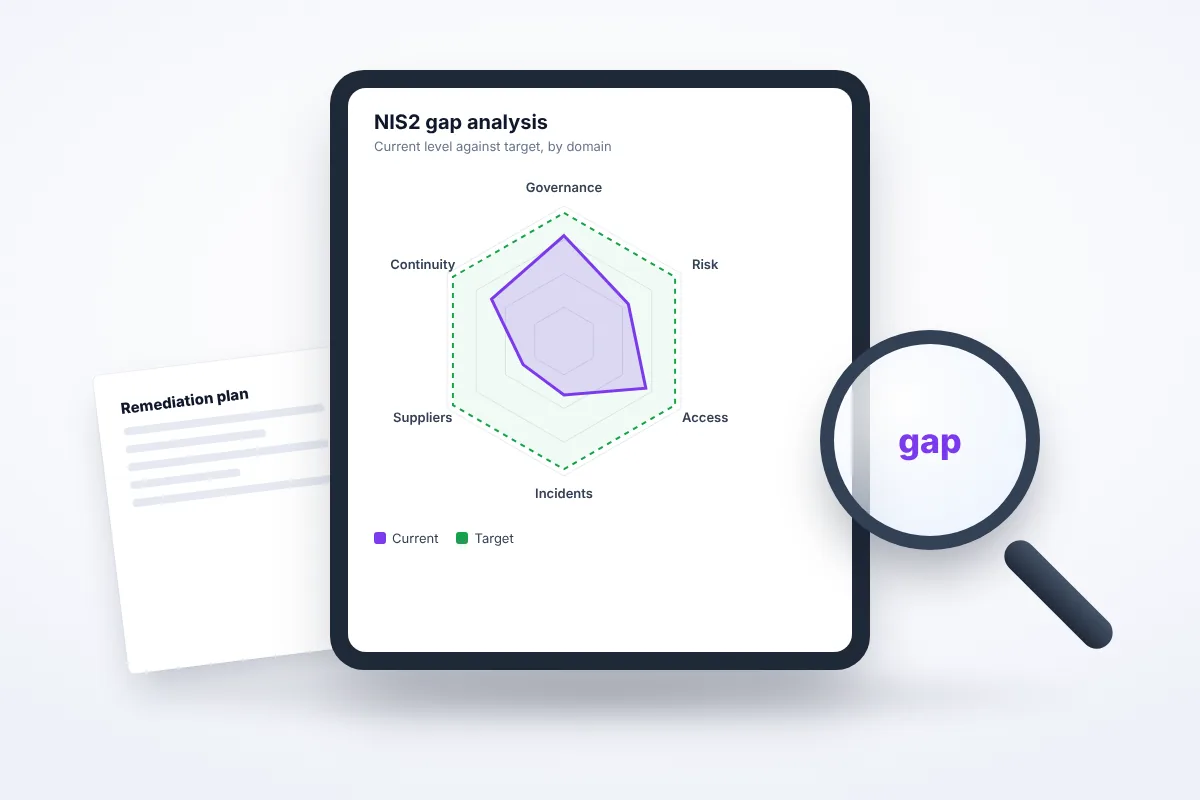
See how far you are from the required measures and what to fix.
See what's includedYou are hereKnow exactly who does what and how to report on the day of an incident.
Request a quote for this step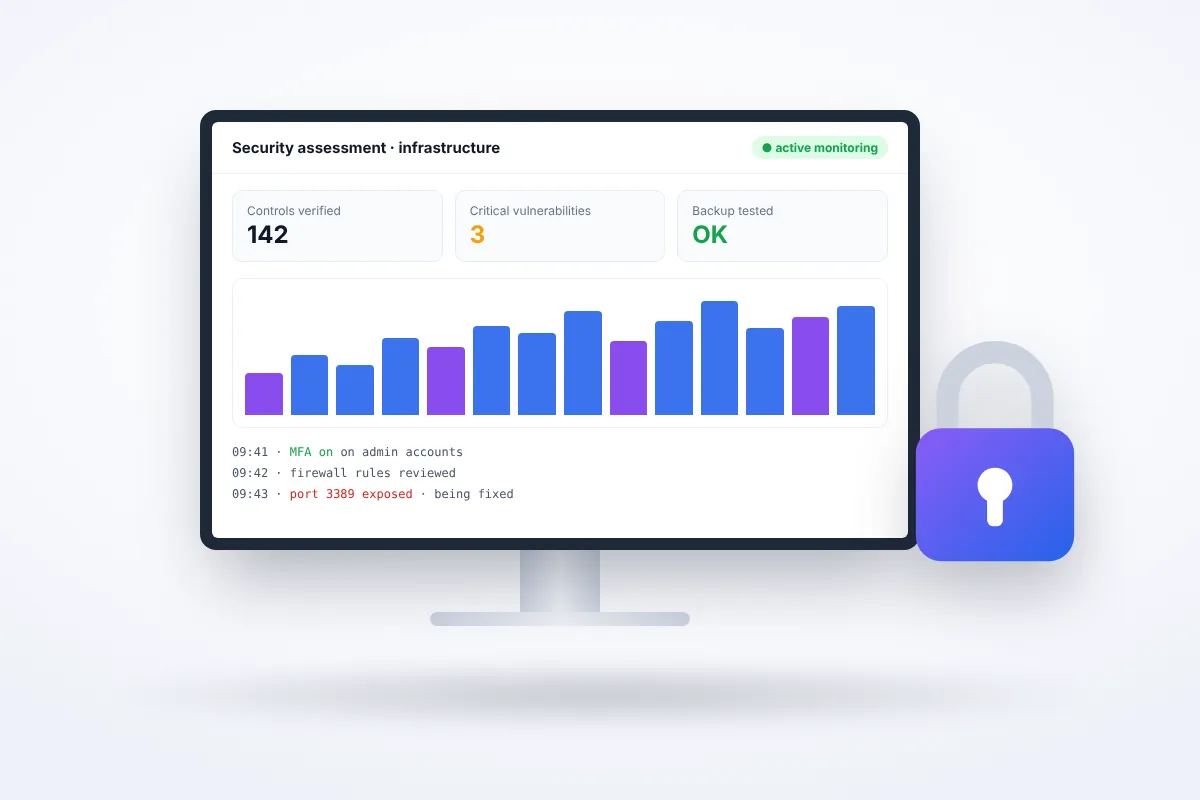
Reach the DNSC audit with your evidence ready and the plan in progress.
See what's includedLeave your details in the form and we will come back with a quote, or call us now.

