

NIS2 gap analysis and pre-audit
We assess your infrastructure, processes and controls against the 6 domains of DNSC Order no. 1/2026.
DNSC has started fining unregistered organizations, up to RON 500,000 for failing to notify.
With the STOREWEB NIS2 cybersecurity audit and NIS2 consulting you find out whether the law applies to you, register with DNSC on time and reach the NIS2 audit with your evidence ready.
Get a quote for NIS2 audit and consulting.
WHY STOREWEB
Since 2008 we have worked with the servers, networks and data of companies and public institutions across Romania. We do cybersecurity on infrastructure we manage every day.
We cover the practical steps required from organizations in Romania, with a clear line between consulting and the regulated DNSC audit.
We assess your infrastructure, processes and controls against the 6 domains of DNSC Order no. 1/2026.
We check whether you are an essential or important entity, prepare the DNSC notification within the 30-day deadline and the documents for your NIS2 officer.
We structure incident response procedures, the PNRISC reporting flow (24h / 72h), backups and recovery plans (business continuity).
We draft NIS2 policies, assess supply chain security and run staff training and phishing simulations.
Select your sector and company size for an indicative classification (essential entity, important entity or supply chain supplier).
The result is indicative and is not legal advice. The official classification is confirmed by analysing your CAEN (NACE) codes and the criteria in GEO no. 155/2024.
Send the result and request a quoteThe regulated audit is performed by a DNSC-certified auditor. We make sure your organization reaches it with the evidence ready.
NIS2 classification, gap analysis, documentation, procedures, technical configuration and the remediation plan.
The periodic or ad-hoc audit set out in GEO no. 155/2024, with the independence required by Article 58.
Legal framework: GEO no. 155/2024, DNSC Order no. 1/2026 and the auditor certification rules.
What a cybersecurity audit checks, who performs the NIS2 audit and how NIS2 consulting helps you pass it.
A cybersecurity audit checks, based on evidence, how well an organization protects its networks, systems, data and services. It does not stop at hardware. It looks at who decides, which rules exist, how they are applied and what happens when an incident occurs.
The result is a clear view of your risks, a list of findings ranked by severity and recommendations management can approve and fund. For a company, a cybersecurity audit is the fastest way to find where it is exposed before an attacker or an inspector does.
Any organization can commission a voluntary cybersecurity audit, to understand its risks or because a large customer asks for one. The regulated NIS2 audit is different. GEO no. 155/2024 requires it for essential and important entities, and only a DNSC-certified cybersecurity auditor can perform it, under strict independence rules.
STOREWEB performs the technical assessment, the NIS2 consulting and the full preparation. When the regulated NIS2 audit comes, your organization already has the documentation, the evidence and a remediation plan in progress, so the auditor's findings are few and easy to close.
A NIS2 audit checks whether the risk management measures required by law are in place and documented. DNSC Order no. 1/2026 groups these measures into 6 domains, from governance and risk analysis to incident handling, continuity and supplier security.
Management accountability is checked too. Management approves the measures, oversees their implementation and takes part in training. That is why a well-prepared NIS2 audit starts with governance documents, not with the firewall.
NIS2 consulting from STOREWEB covers the whole journey. We determine whether you are an essential or important entity, prepare your DNSC registration, carry out the NIS2 gap analysis and the risk level assessment, and write the incident response and reporting procedures.
The difference from paper-only consulting is the technical side. We have worked with servers, networks, hosting and backups since 2008, so our cybersecurity recommendations can actually be implemented, not just written in a report.
Many small companies are not directly covered by NIS2 but work for companies that are. Those customers must check supply chain security, so they ask suppliers for concrete evidence about passwords, access, backups, updates and incident handling.
A cybersecurity audit done early helps these suppliers answer customer questionnaires quickly and keep their contracts. For a small company, cybersecurity becomes a commercial advantage, not just an obligation.
We start with a conversation about your business, digital services and infrastructure. Together we agree which systems are in scope and what evidence already exists. Then come interviews, document review and technical checks on configurations, accounts, network and backups.
At the end you receive the cybersecurity audit report, with findings ranked by risk level, and a remediation plan with priorities and deadlines. If you wish, we implement the technical measures ourselves, through IT outsourcing or on dedicated servers managed by our team.
The notification to DNSC is due within 30 days of the date the law starts applying to your organization. DNSC decides on registration within 60 days for essential entities and 150 days for important entities.
After the decision comes the risk level assessment within 60 days, then the maturity self-assessment within another 60 days. Essential entities submit the remediation plan within 30 days. For failing to notify, DNSC has announced fines of up to RON 500,000.
The price depends on the number of sites, systems and critical suppliers, on existing documentation and on what you need, from classification and registration to a full gap analysis or NIS2 audit preparation. A company with one office and a few servers needs less time than a group with several sites.
Fill in the form above, we have a short call and you receive a quote for the cybersecurity audit or NIS2 consulting, with stages, deliverables and timeline clearly set out.
Answers for organizations considering a cybersecurity project.
It is a systematic assessment of the policies, procedures and protection measures applied to networks and information systems. For a regulated audit under Article 58 of GEO no. 155/2024, the auditor must hold a valid DNSC certification.
No. The preliminary assessment, gap analysis and NIS2 readiness consulting are consulting services. They are not a regulated audit, do not issue a certificate and do not officially certify the organization's compliance.
Not automatically. It depends on the sectors and activities in the legal framework, the size criteria and the organization's specific circumstances. Each entity must analyse its own classification.
It depends on the number of systems, infrastructure complexity, availability of documents and evidence, authorized access and project goals. The timeline can be estimated once the scope is defined.
A description of your business, your digital services, general information about the infrastructure and your goals are useful. Do not send passwords, private keys or sensitive data through the public form.
Consulting and implementation can be contracted depending on scope and compatibility of activities. If a regulated audit is later planned for the same organization or systems, auditor independence and legal restrictions must be assessed separately before contracting.
Classification as an essential or important entity, DNSC registration, the NIS2 gap analysis and risk level assessment, the required policies and procedures, incident response procedures and preparing evidence for the NIS2 audit.
Essential and important entities in the sectors listed in GEO no. 155/2024. The regulated NIS2 audit is performed by a DNSC-certified auditor; STOREWEB prepares your organization for it.
Each step prepares the next one. You can start with any of them, depending on where your organization is now.
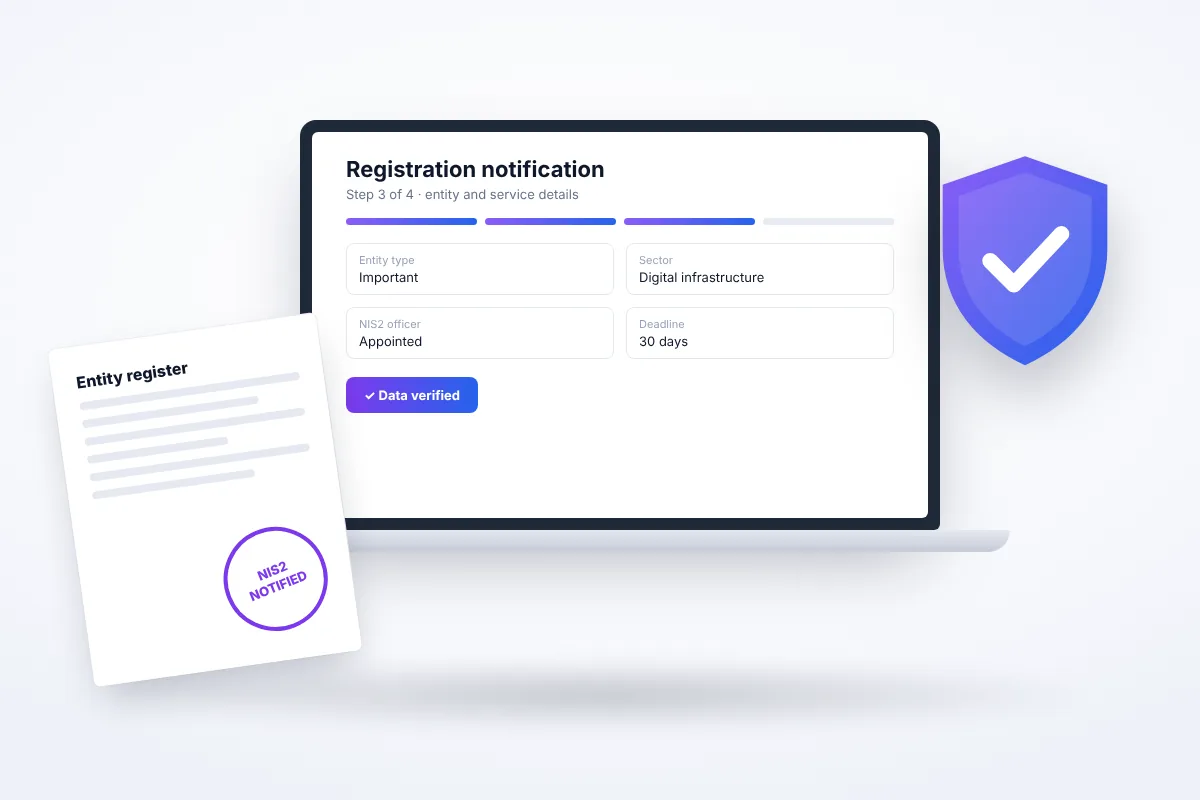
Find out whether NIS2 applies and notify DNSC within the 30 days.
See what's included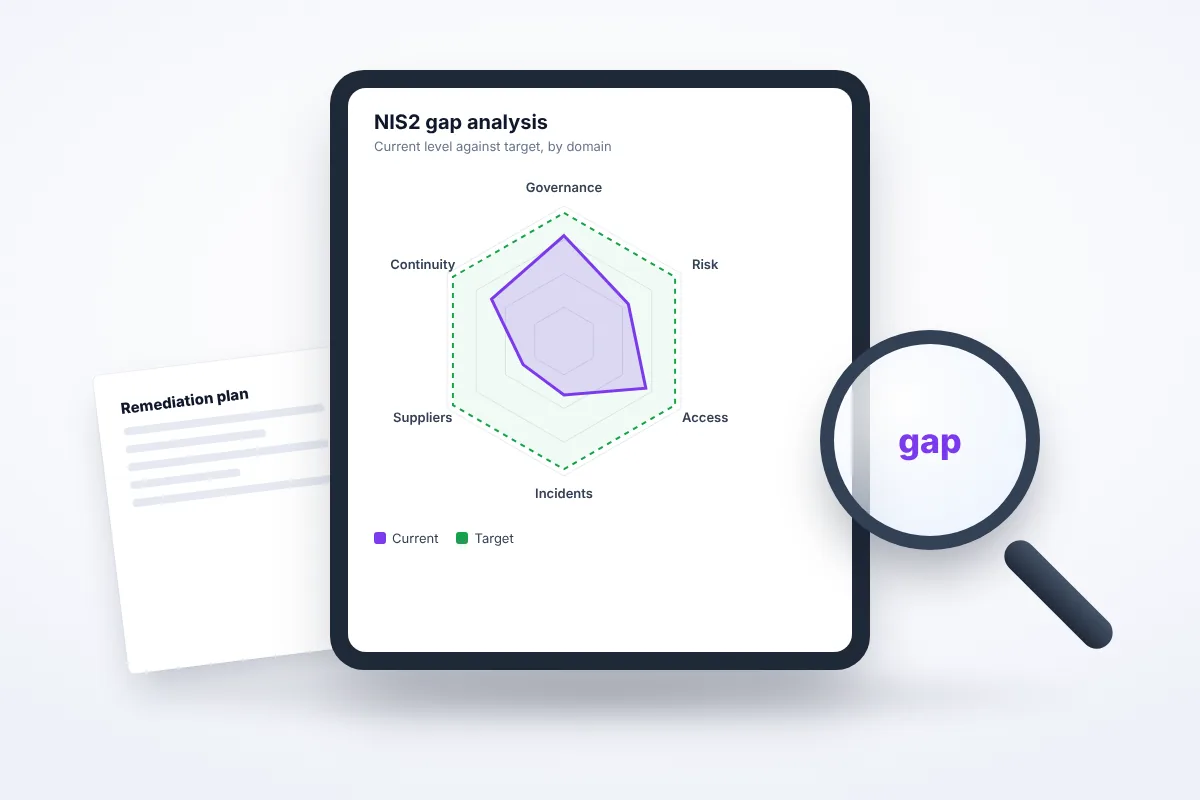
See how far you are from the required measures and what to fix.
See what's included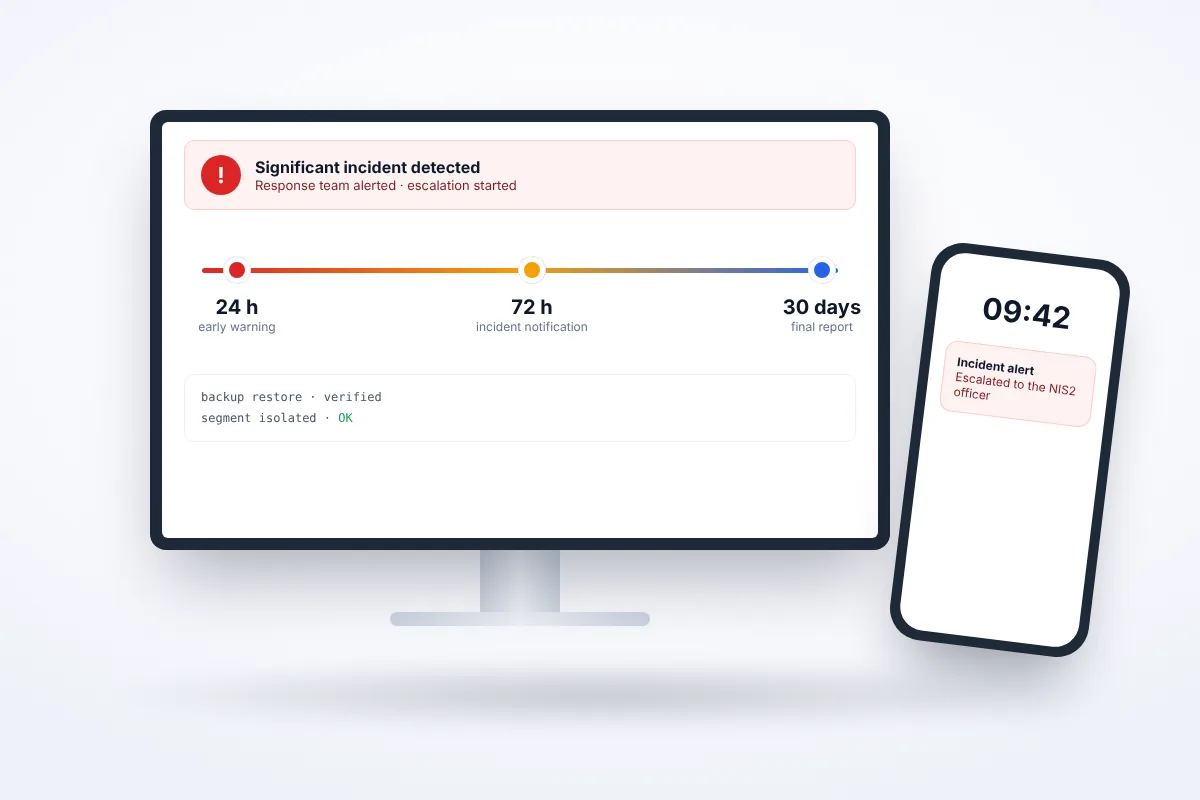
Know exactly who does what and how to report on the day of an incident.
See what's includedYou are hereReach the DNSC audit with your evidence ready and the plan in progress.
Request a quote for this stepLeave your details in the form and we will come back with a quote, or call us now.

