

Gap analysis across 6 domains
We assess Governance, Identify, Protect, Detect, Respond and Recover against GEO no. 155/2024 and DNSC Order no. 1/2026.
DNSC has started fining unregistered organizations, up to RON 500,000 for failing to notify.
A NIS2 gap analysis shows how far you are from the measures in DNSC Order no. 1/2026. We prepare the evidence for your NIS2 self-assessment and deliver the remediation plan, for organizations across Romania.
Get a quote for NIS2 gap analysis and self-assessment.
WHY STOREWEB
Since 2008 we have worked with the servers, networks and data of companies and public institutions across Romania. We do cybersecurity on infrastructure we manage every day.
Every project is tailored to your organization's size, infrastructure and sector.
We assess Governance, Identify, Protect, Detect, Respond and Recover against GEO no. 155/2024 and DNSC Order no. 1/2026.
We structure the risk register, the critical asset inventory and the evidence needed for the self-assessment on the SecureRO / CyFun platform.
We prioritize technical and organizational measures by risk, impact and budget, with clear owners and deadlines before the certified audit.
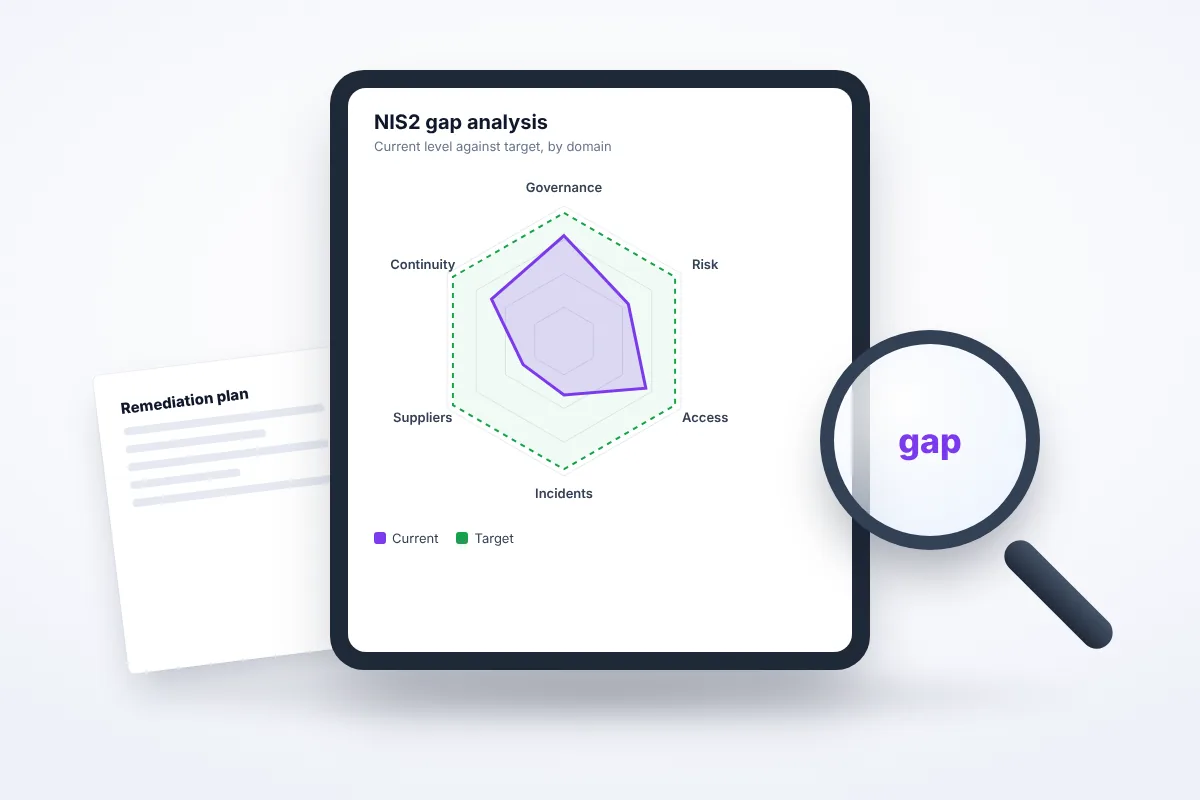
After registration come three deliverables with deadlines. The gap analysis comes first, so you know what you will declare and with what evidence.
| Assessment | Legal basis | Deadline |
|---|---|---|
| 1. Risk level assessment | DNSC Order no. 2/2025, with the ENIRE@RO tool | 60 days from notification of the registration decision |
| 2. Maturity self-assessment | DNSC Order no. 1/2026, in force since 27 August 2026, covering risk management measures and the self-assessment methodology | 60 days from submission of the risk assessment |
| 3. Remediation measures plan | GEO no. 155/2024; essential entities submit it to DNSC | 30 days from the self-assessment |
Deadlines are those in GEO no. 155/2024 and the DNSC orders as publicly communicated. Check the current version before making a decision.
DNSC representatives have stated publicly that self-assessments may be compared with what is found during an inspection and, later, with the circumstances of any incident. The gap analysis shows where you stand against the measures in Order no. 1/2026 and what evidence supports each answer.
SecureRO is DNSC's platform with a self-assessment questionnaire based on the CyberFundamentals (CyFun) framework and a free toolset. We use it as a starting point where the organization is already registered.
If you have not notified DNSC yet, start with DNSC registration and the deadline timeline.
What the analysis checks, how it prepares you for the NIS2 self-assessment and ENIRE@RO, and what you get at the end.
The analysis compares what your organization does today with the measures required by GEO no. 155/2024 and DNSC Order no. 1/2026. The result shows, domain by domain, where you are covered, where you have gaps and which evidence is missing.
Unlike a ticked box on a questionnaire, the analysis checks real evidence such as approved policies, configurations, logs, supplier contracts and restore tests.
The NIS2 maturity self-assessment is sent to DNSC after the risk level assessment, within the deadline set by the DNSC orders. DNSC has stated publicly that self-assessments may be compared with what is found during an inspection.
That is why the NIS2 gap analysis comes before the self-assessment. You know what you declare and have evidence for every answer.
DNSC Order no. 2/2025 sets the risk level assessment methodology, using the ENIRE@RO tool. The assessment is due within 60 days of the registration decision.
We prepare the data ENIRE@RO asks for, the critical asset inventory and the risk register, so the assessment is done once and done right.
We analyse governance, asset and risk identification, protection, detection, incident response and recovery. For each domain we record the current level, the target level and what needs to be done.
We check the technical side directly on the infrastructure, with a team that has managed servers and networks since 2008.
Companies not directly covered by NIS2 increasingly receive security questionnaires from their large customers. An analysis done early gives you the answers and evidence they ask for.
For SMEs we offer a shorter version focused on what customers usually ask for, with a remediation plan that fits a realistic budget.
Duration and price depend on the number of sites, systems and critical suppliers and on existing documentation. A company with a single office finishes faster than a group with several sites.
We work remotely with organizations across Romania. Fill in the form above and get a quote with clearly defined stages and deliverables.
The analysis covers all six domains of the national framework (Governance, Identify, Protect, Detect, Respond and Recover), identifying what is missing and what must be implemented.
The gap analysis is a preliminary readiness assessment and internal diagnosis. The regulated audit (Articles 57-58 of GEO no. 155/2024) is performed only by a certified auditor listed by DNSC.
An executive summary for management, the gap matrix against NIS2 requirements, a preliminary risk register and a prioritized plan of technical and organizational measures.
Essential and important entities in the DNSC register submit the maturity self-assessment after the risk level assessment, under the DNSC orders.
Yes. Interviews and document review happen online, and technical checks through controlled access. We work with organizations across Romania.
Each step prepares the next one. You can start with any of them, depending on where your organization is now.
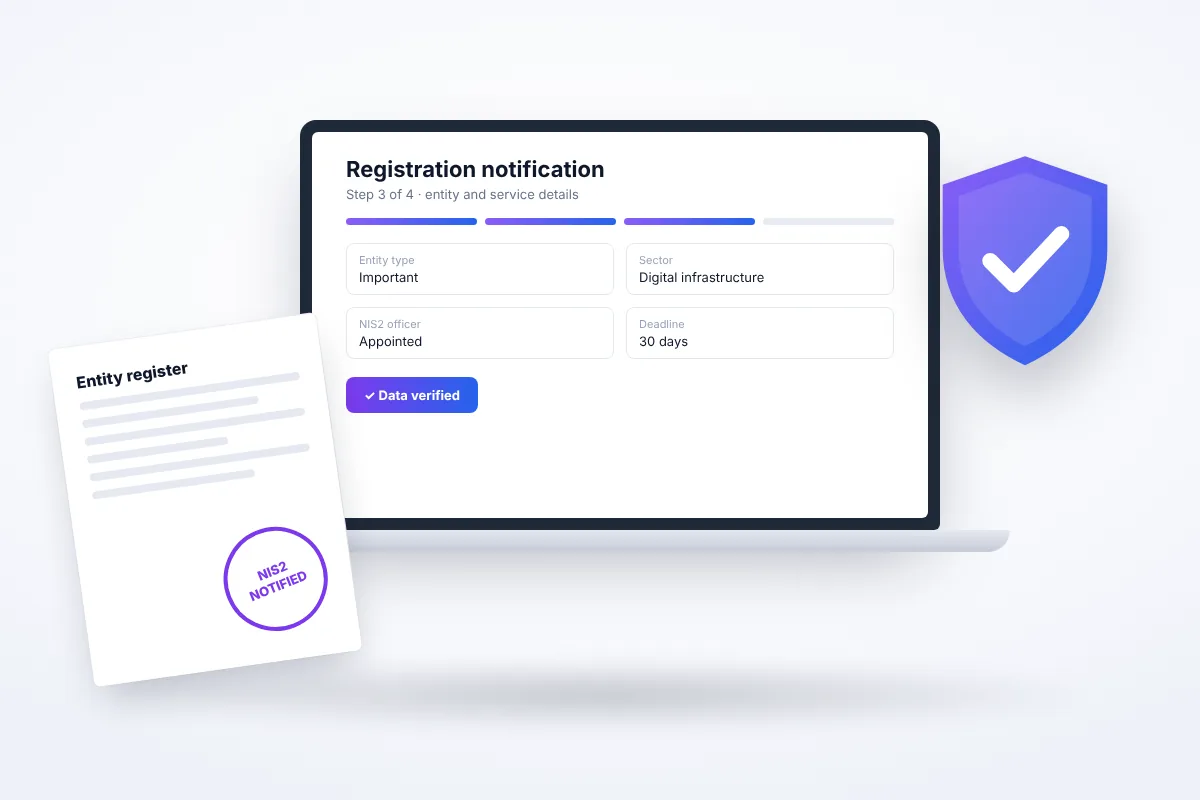
Find out whether NIS2 applies and notify DNSC within the 30 days.
See what's includedYou are hereSee how far you are from the required measures and what to fix.
Request a quote for this step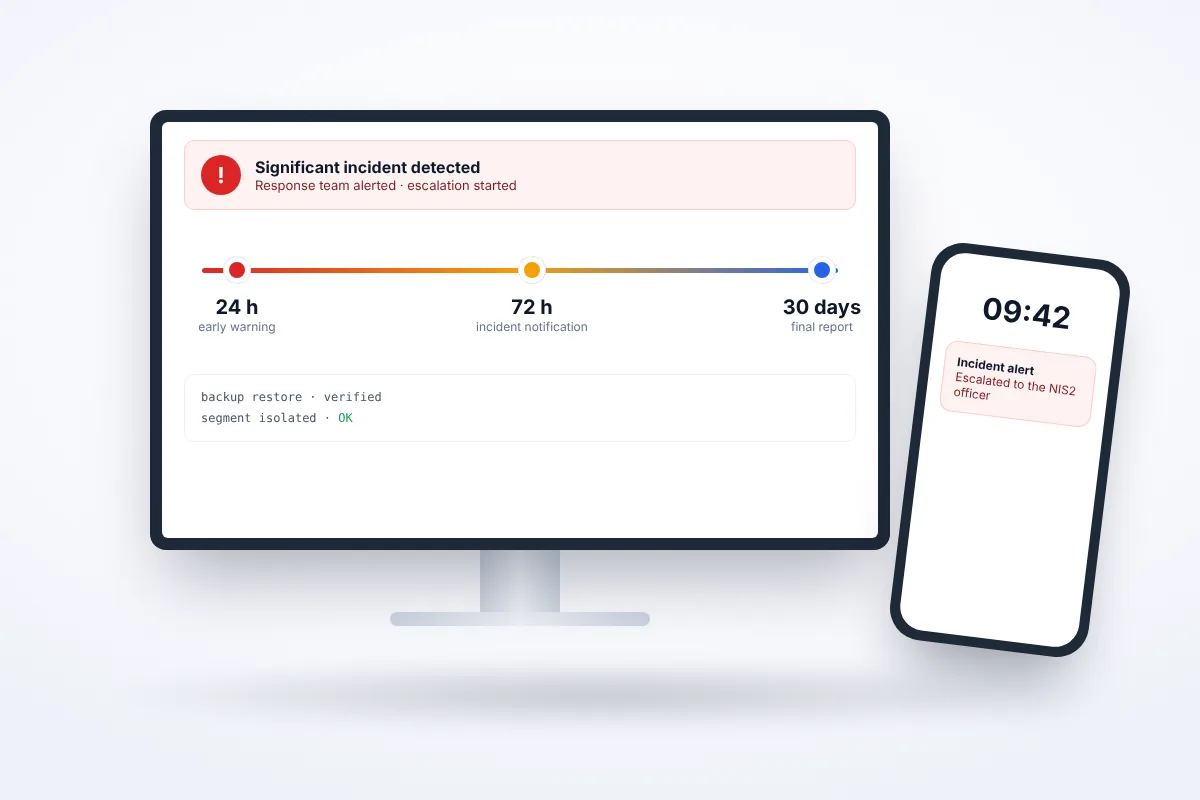
Know exactly who does what and how to report on the day of an incident.
See what's included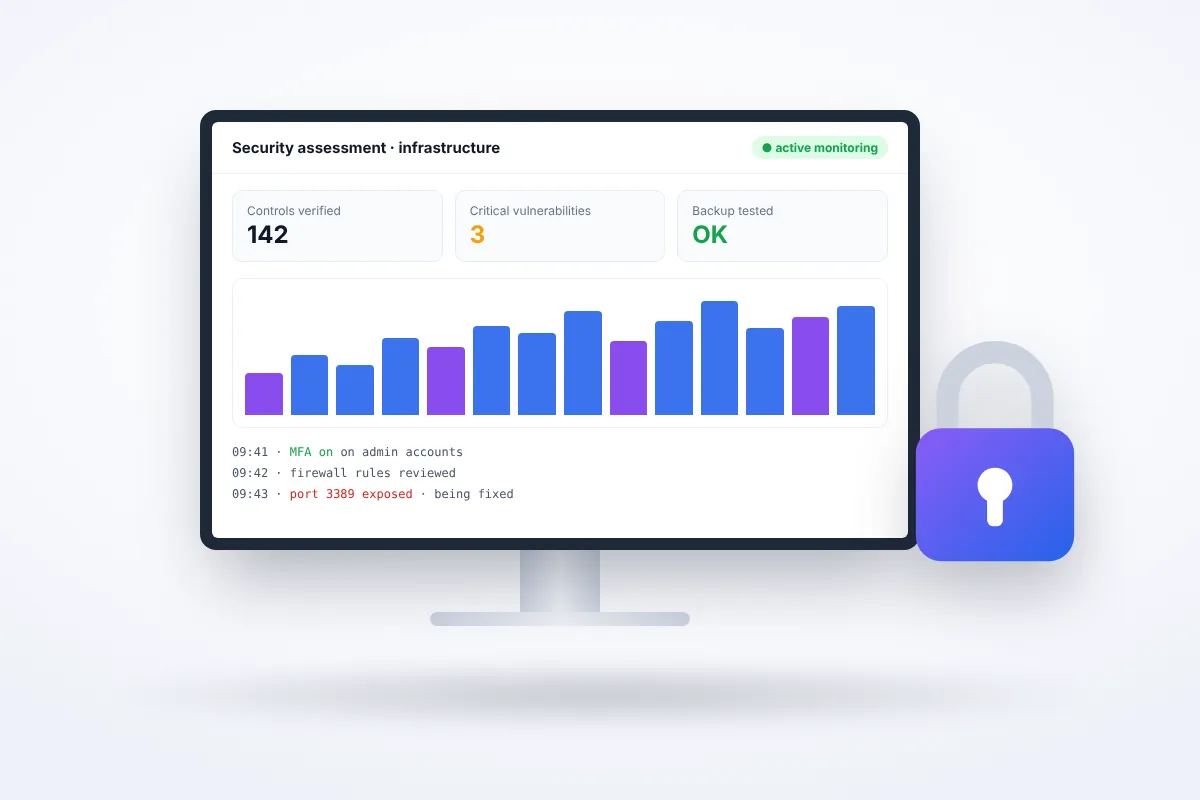
Reach the DNSC audit with your evidence ready and the plan in progress.
See what's includedLeave your details in the form and we will come back with a quote, or call us now.

