01 · ATTACK MAP
See where attacks come from
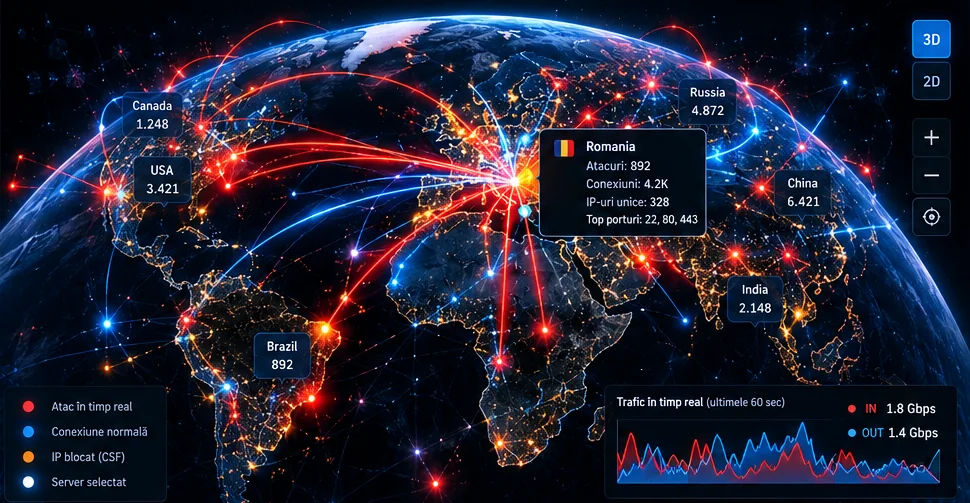
The 3D and 2D map shows in real time which countries connections and attacks on your servers come from, with the number of attacks per country.
NIS2 requires an early warning to DNSC within 24 hours. Without monitoring, you find out about an attack too late.
Real-time cybersecurity monitoring: see attacks on your servers and workstations on a map, dangerous IPs are blocked automatically in the firewall, and you get alerts and reports. For companies and institutions across Romania.
Request a monitoring offer
You get an offer based on the number of servers and workstations.
TEAM AND CERTIFICATIONS
Since 2008 we have worked with the servers, networks and data of companies and institutions across Romania. Our specialists hold Cisco CCNA 1, 2, 3 and 4 certificates, and we do cybersecurity on the infrastructure we run every day.
STOREWEB SOC collects data from your servers and workstations: attacks, connections, IPs blocked by the firewall and traffic per service. See what is happening now and what happened yesterday.
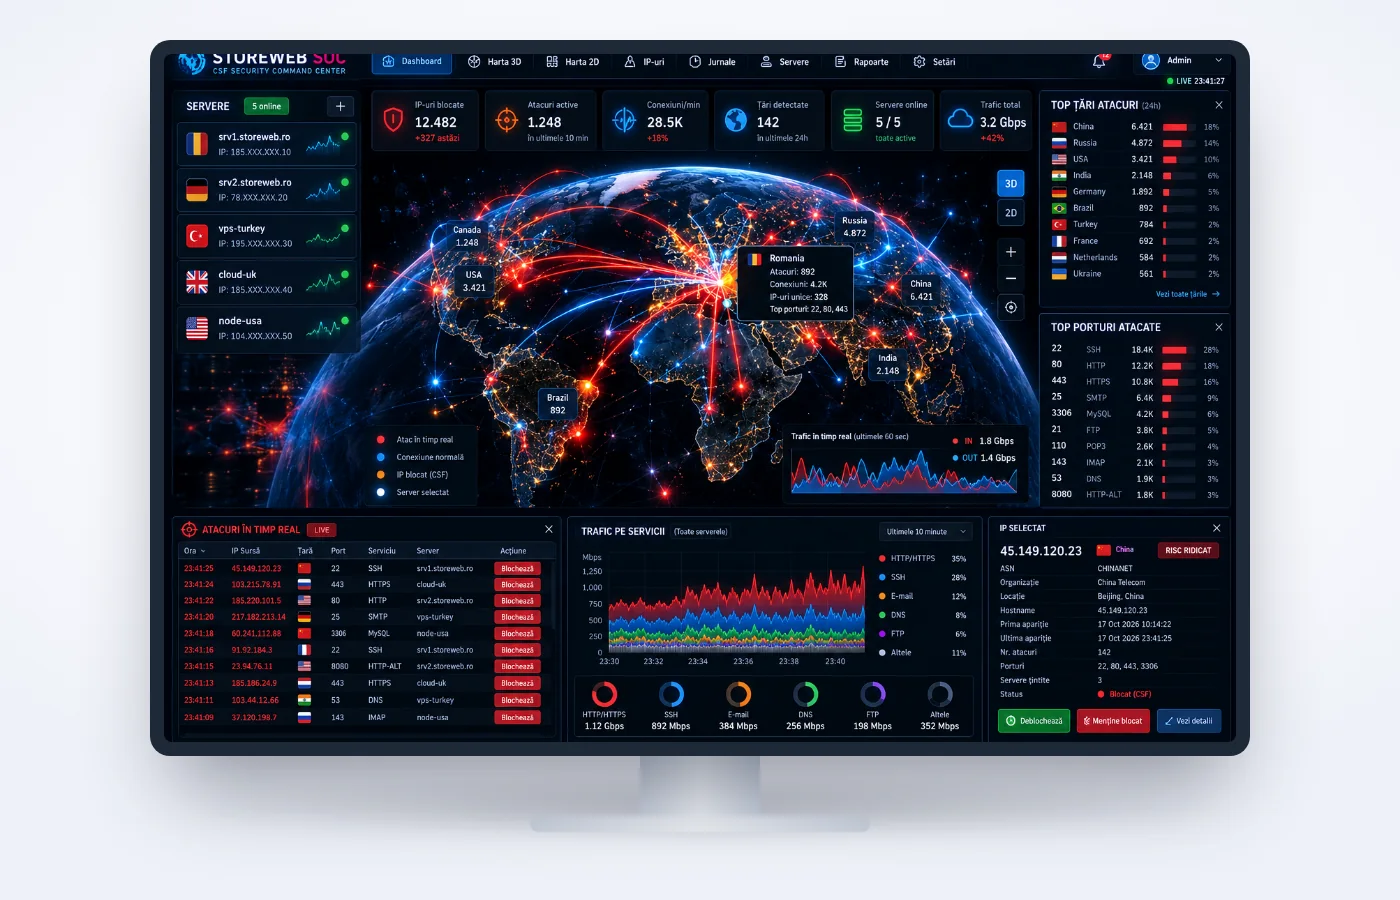
The information you need to react quickly and to have evidence during an inspection.
The 3D and 2D map shows in real time which countries connections and attacks on your servers come from, with the number of attacks per country.
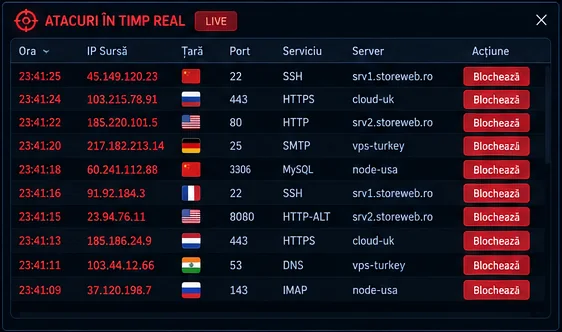
Every attack appears with the time, source IP, country, port, service and targeted server. You block a suspicious IP straight from the list.
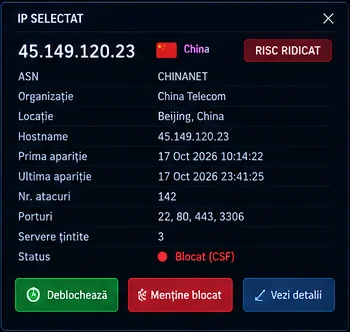
For every IP you see the provider, location, first and last appearance, number of attacks, ports tried and servers targeted.
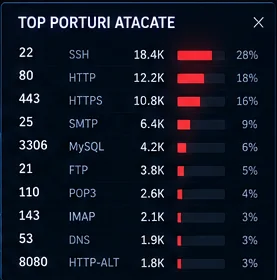
The top attacked ports and services (SSH, HTTP, email, databases) shows you where to harden your configuration.
Start with what matters most to you and expand at any time. You get a written offer based on the number of servers and workstations.
Dedicated servers, VPS or cloud, with attacks on the map, automatic firewall blocking, alerts and reports.
Request an offerYour employees' workstations, with security events on the same screen and alerts on what matters.
Request an offerServers and workstations in a single SOC, with a periodic report written as evidence for the NIS2 self-assessment.
Request an offerDNSC Order no. 1/2026 also checks the Detection domain. Monitoring gives you the logs and evidence you need for the self-assessment and for an inspection.
You find out about the attack when the server goes down or when a client calls you. The 24-hour deadline for the early warning has already started.
You see the attack when it starts, the IP is blocked automatically, and the log gives you the data for reporting to DNSC.
What monitoring does, how it helps with NIS2 and what you get from STOREWEB SOC.
Cybersecurity monitoring continuously tracks what happens on your servers and network: connections, login attempts, port scans and attacks. The goal is to see an attack in the first minutes, not after it has caused damage.
STOREWEB SOC brings this data together on a single screen, with the attack map, the list of blocked IPs and traffic per service, for all your servers and workstations.
Monitoring without a response only counts attacks. That is why we connect monitoring to the firewall: IPs that try passwords, scan ports or send suspicious traffic are blocked automatically.
From the SOC you can block an IP manually, unblock it or keep it blocked, with the full history of its attacks.
An in-house security operations center (SOC) means people and expensive tools. For a small or medium-sized company, outsourced monitoring offers the same visibility without hiring a team.
You can start with critical servers and then extend monitoring to all servers and workstations. We work with companies and institutions across Romania.
Essential and important entities must detect incidents and send an early warning to DNSC within 24 hours. Without monitoring, the deadline starts running before you know about the incident.
The SOC logs help you with incident reporting through PNRISC and with the NIS2 self-assessment, in the Detection chapter.
We monitor dedicated, VPS or cloud servers with web, email, database and remote access services, as well as your employees' workstations. On the same interface you see all servers and workstations, whatever country they are in.
If your servers are hosted at STOREWEB, on dedicated servers or through IT outsourcing, we start faster because we already manage the infrastructure.
The price depends on the number of servers and workstations, the services monitored and how often you want reports. You pay monthly, with no upfront investment in equipment.
Fill in the form above and you get an offer for cybersecurity monitoring, with what it includes and the cost per server and per workstation.
Most attacks give warning signs before they succeed. Repeated password attempts, port scans, odd requests to your website or sudden traffic from countries you don't work with are the signs monitoring catches in the first minutes.
In STOREWEB SOC you see every sign on the map and in the attack list, with the IP, the targeted service and the time. Dangerous IPs are blocked automatically and you receive an alert.
The SOC history shows where the attack came from, which services it tried and how long it lasted. This is exactly the data you need to decide whether the incident is significant and must be reported to DNSC.
We set the isolation, investigation and reporting steps in advance in the CSIRT and PNRISC reporting procedures, so the response does not depend on improvisation.
Access to STOREWEB SOC with the attack map, the real-time attack list, blocked IPs, traffic per service and the profile of each IP, plus automatic firewall blocking, alerts and reports.
No. It uses and complements them. The firewall blocks, while monitoring shows you what was blocked, where attacks come from and which services are targeted.
Yes. In the SOC you see why an IP was blocked and you can unblock it or keep it blocked in one click.
Yes, for the Detection domain and for incident reporting. The logs give you the data required for the early warning and for the notification to DNSC.
No. We also monitor servers hosted with other providers. If they are with us, onboarding is faster.
Yes. Monitoring is done remotely, for companies and institutions in any county.
Each step prepares the next one. You can start with any of them, depending on where your organization is now.
Find out whether NIS2 applies and notify DNSC within the 30 days.
See what's included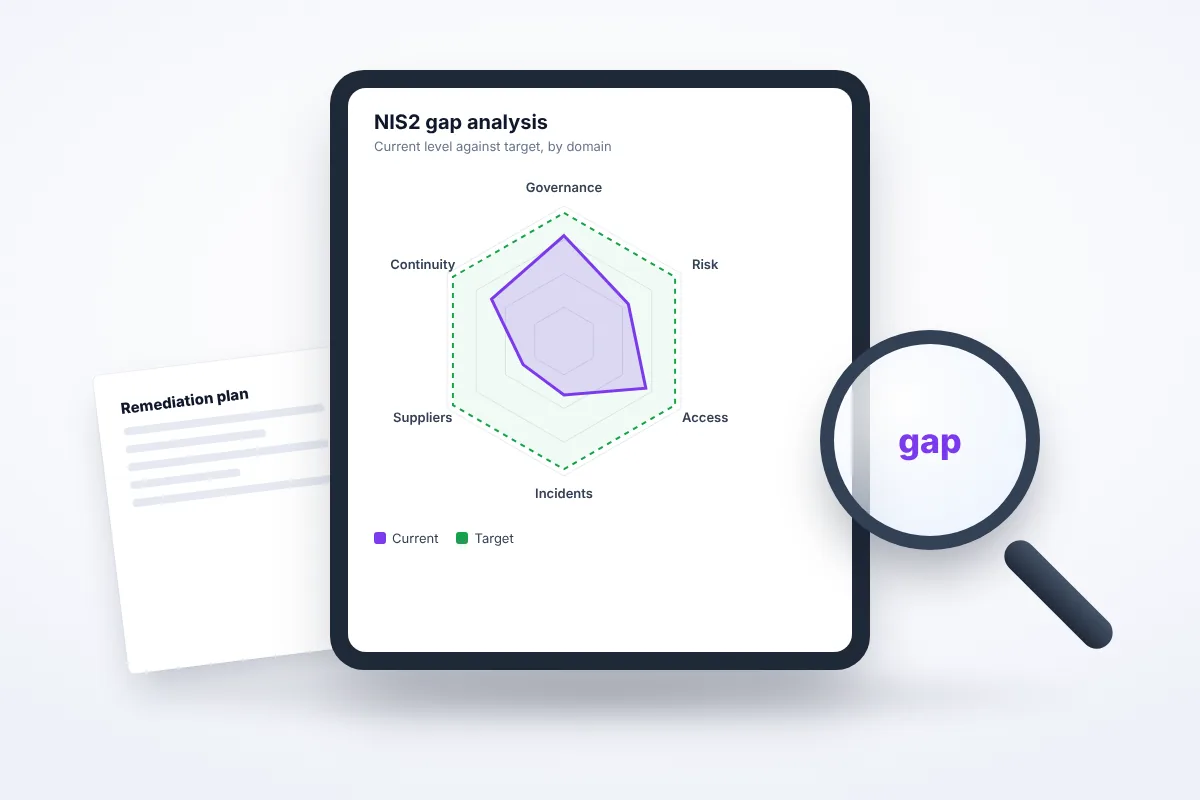
See how far you are from the required measures and what to fix.
See what's included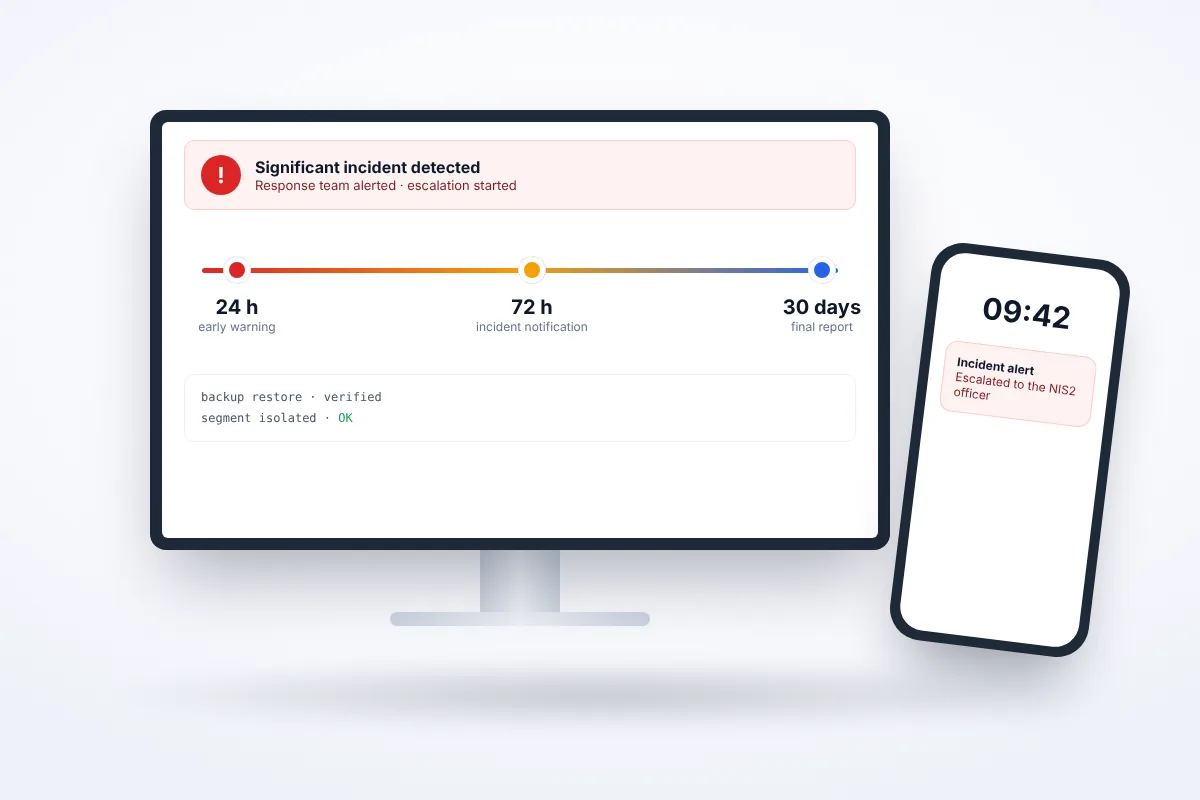
Know exactly who does what and how to report on the day of an incident.
See what's included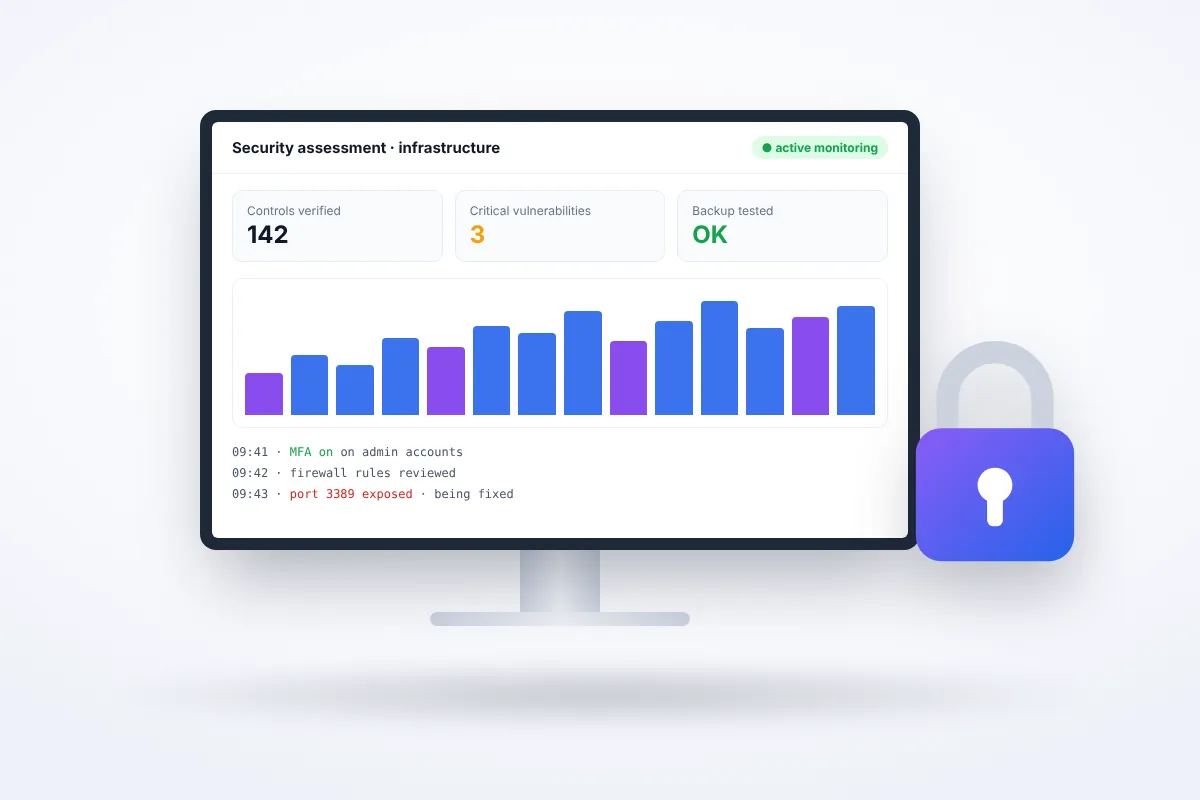
Reach the DNSC audit with your evidence ready and the plan in progress.
See what's includedLeave your details in the form and get an offer for monitoring.